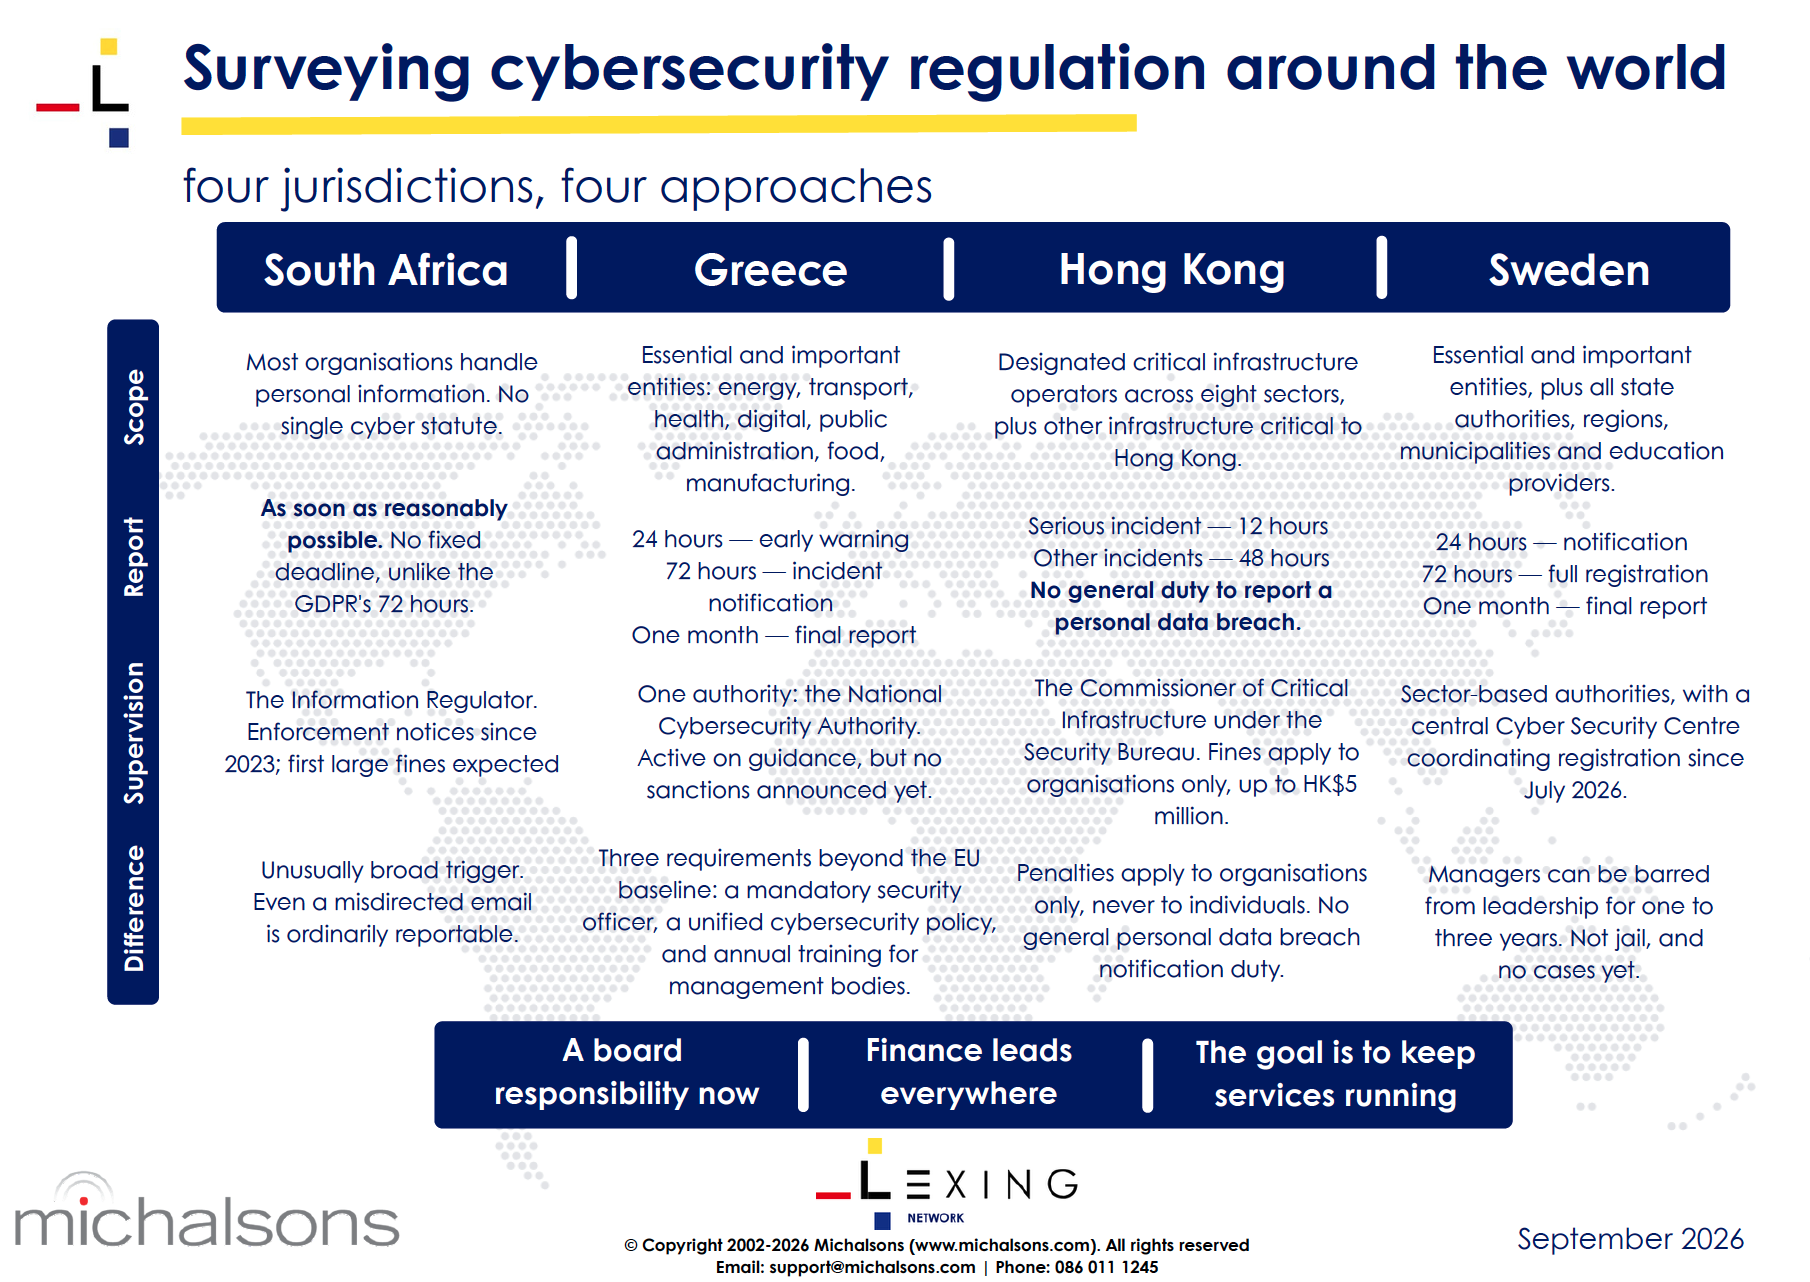
Cybersecurity has become a legal and compliance issue, not just a technical one. Organisations across the world now have to deal with a growing set of cybersecurity laws, regulations, reporting duties, governance requirements, sector rules, and enforcement risks. Often in multiple jurisdictions.
Many countries do not address cybersecurity through a single statute. Instead, organisations often face a layered framework comprising data protection law, cybercrime law, critical infrastructure rules, incident reporting duties, sector-specific obligations, and information security standards.
We’ve engaged with Lexing Network experts to bring you this overview of Cybersecurity regulations around the world. We’ve tackled four countries so far and will add to them over the coming months.
We have focused on
- How cybersecurity is regulated in each country.
- The main laws, regulations, or standards that organisations need to know.
- The incident reporting duties that apply after a cybersecurity incident.
- The main compliance challenges organisations face.
- What makes each country different from others regarding cybersecurity regulations.
- How active their supervisory authorities are.
- Developments organisations should watch for in your jurisdiction.
Access our easy to follow Infographics
From the recent interview with Padraig Walsh.
From the interview with Nikolaos A. Papadopoulos
From the interview with Katarina Bohm Hallkvist

Actions to take
- Stay up-to-date as we add further country summaries by signing up to our newsletter.
- Make sure you comply by joining our Cybersecurity compliance programme.
- Let us know what country we should focus on next.